Foiling cyberattacks
Closing security loopholes and prepping backup plans are your first line of defense.
Cyberattacks on healthcare systems are on the rise and present a growing threat to everything from data to lost time to the lives and health of patients. Hospitals and healthcare systems have seen an average of more than 600 hacking or security incidents annually in recent years. In 2024 alone, more than 275 million records were compromised. The average cost of a healthcare data breach in the U.S. in 2025 was $10.22 million, up 9.2% from the year before.
The question is not if a cyberattack will occur, but when. Having an emergency plan in place is critical to the survival of your system and the patients you are there to help. Creating that plan will be the subject of the Tuesday session, “Code Dark: Are You Prepared for a Hospital System Cyberattack?”
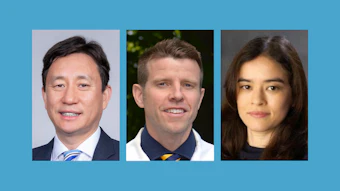
Session director Sagar Mungekar, MD, Associate Professor and Vice Chair of Systems and Analytics at Robert Wood Johnson Medical School at Rutgers University in New Brunswick, New Jersey, said most cyberattacks fall into one of two categories.
“One is unauthorized access of the electronic health record (EHR) system to obtain protected health information. The information is then sold on the black market,” he said. “The other type is accessing the EHR and either rendering it unusable or encrypting the data so that it cannot be accessed. Hackers then demand a ransom to restore access.”
The second type of attack, called ransomware attacks, can be especially dangerous, according to Dr. Mungekar, as it prevents healthcare professionals from obtaining or retrieving medical information about patients. This in turn impairs their ability to provide patients with medical care.
“Approximately two-thirds of attacks are of this type,” he said. “These are truly threat-to-life crimes that put patient safety at risk and have been shown to result in increased mortality rates.”
Because these attacks are more difficult to stop, being prepared for them when they do occur can help minimize harm, said session presenter Anthony Fritzler, MD, FASA, anesthesiologist at Akron Children’s Hospital. One of the best steps a healthcare system can take is to have a firm policy in place that outlines what to do in the event of a cyberattack.
“It is essential for healthcare systems to have standard work instructions in place that facilitate an uninterrupted transition in operations during a cyberattack,” Dr. Fritzler said. “Who are the interested parties? Yes, anesthesiologists and surgeons, but what about pharmacy, patient transport, and the laboratory? The primary systemic goals should generally be to protect unaffected systems and facilitate communication during an attack.”
Although technology continues to move forward, one of the key tools for dealing with a cyberattack requires seemingly taking a step backward. Paper can be your biggest ally in the event of an attack, said session presenter Olga Leavitt, MD, anesthesiologist at Ann & Robert H. Lurie Children’s Hospital of Chicago.
“You should have plans for communication methods throughout the system — paper charting, the development of paper order sets, and [physician] access to medications are of paramount importance for an anesthesiology department,” she said. “Having easy-to-access paper records is essential. Order sets may contain dozens of individual orders, which most clinicians would not be able to recreate by memory. It is important to have blank intraoperative anesthesia records to document vital signs, medications, and more.”
Although much of the session will focus on dealing with the aftermath of an attack, there are steps that health systems can take to prevent an attack. One simple step involves training your teams to mitigate human vulnerabilities that are inherent in any health system, said session presenter Lindsey Rutland, MD, FASA, anesthesiologist at Dell Children’s Medical Center in Austin, Texas.
“User account compromise is the most common attack vector,” she said. “Using shared passwords, creating simple passwords, not logging off machines, using a compromised network, and falling for phishing attacks are all ways hackers can gain access. Sometimes service or administrative accounts are left with generic logins from the manufacturers.”
One tool that can help secure this area is multifactor authorization, often using a third-party application to allow the user to log in only after a code has been sent to a secure email or mobile device. But a more important tool, Dr. Mungekar said, is regular and consistent training for both preventing an attack and dealing with its aftermath.
“While most hospitals have downtime contingency plans, those are usually designed to address short-term, well-defined network outage periods during maintenance or an upgrade, not cyberattacks,” he said. “Training and planning for a cyberattack should be ongoing. For each new order set, workflow, or process, there should be a downtime pathway. A simulation should occur at least yearly to determine opportunities both for an attack and for improvement in the plan.”